
Microsoft Azure Flaws Could Have Let Hackers Take Over Cloud Servers

Image result for microsoft azure hack"
Cybersecurity researchers at Check Point today disclosed details of two recently patched potentially dangerous vulnerabilities in Microsoft Azure services that, if exploited, could have allowed hackers to target several businesses that run their web and mobile apps on Azure.
Azure App Service is a fully-managed integrated service that enables users to create web and mobile apps for any platform or device, and easily integrate them with SaaS solutions, on-premises apps to automate business processes.
According to a report researchers shared with The Hacker News, the first security vulnerability (CVE-2019–1234) is a request spoofing issue that affected Azure Stack, a hybrid cloud computing software solution by Microsoft.
If exploited, the issue would have enabled a remote hacker to unauthorizedly access screenshots and sensitive information of any virtual machine running on Azure infrastructure — it doesn’t matter if they’re running on a shared, dedicated or isolated virtual machines.
According to researchers, this flaw is exploitable through Microsoft Azure Stack Portal, an interface where users can access clouds they have created using Azure Stack.
By leveraging an insure API, researchers found a way to get the virtual machine name and ID, hardware information like cores, total memory of targeted machines, and then used it with another unauthenticated HTTP request to grab screenshots, as shown.
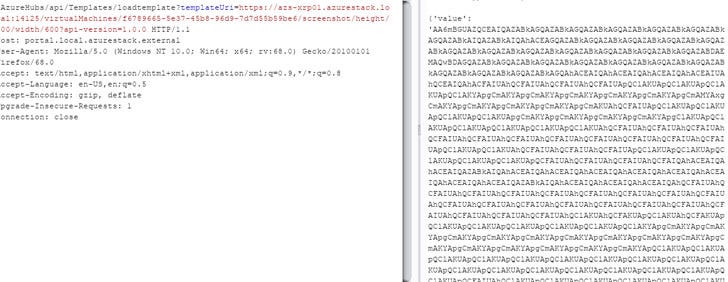
Whereas, the second issue (CVE-2019–1372) is a remote code execution flaw that affected the Azure App Service on Azure Stack, which would have enabled a hacker to take complete control over the entire Azure server and consequently take control over an enterprises’ business code.
What’s more interesting is that an attacker can exploit both issues by creating a free user account with Azure Cloud and running malicious functions on it or sending unauthenticated HTTP requests to the Azure Stack user portal.
Check Point published a detailed technical post on the second flaw, but in brief, it resided in the way DWASSVC, a service responsible for managing and running tenants’ apps and IIS worker processes, which actually run the tenant application, communicate with each other for defined tasks.
Since Azure Stack failed to check the length of a buffer before copying memory to it, an attacker could have exploited the issue by sending a specially crafted message to DWASSVC service, allowing it to execute malicious code on the server as the highest NT AUTHORITY/SYSTEM privilege.
“So how can an attacker send a message to DWASSVC (DWASInterop.dll)? By design, when running the C# Azure function, it runs in the context of the worker (w3wp.exe),” the researchers said.
“This lets an attacker the possibility to enumerate the currently opened handles. That way, he can find the already opened named pipe handle and send a specially crafted message.”
Check Point researcher Ronen Shustin, who discovered both vulnerabilities, responsibly reported the issues to Microsoft last year, preventing hackers from causing severe damage and chaos.
After patching both issues late last year, the company awarded Shustin with 40,000 USD under its Azure bug bounty program.

Check the original article: https://thehackernews.com/

Comments

Popular posts from this blog

Bogus Android Clubhouse App Drops Credential-Swiping Malware

The malicious app spreads the BlackRock malware, which steals credentials from 458 services — including Twitter, WhatsApp, Facebook and Amazon. Researchers are warning of a fake version of the popular audio chat app Clubhouse, which delivers malware that steals login credentials for more than 450 apps. Clubhouse has burst on the social media scene over the past few months, gaining hype through its audio-chat rooms where participants can discuss anything from politics to relationships. Despite being invite-only, and only being around for a year, the app is closing in on 13 million downloads . However, as of now the app is only available on Apple’s App Store mobile application marketplace — there’s no Android version yet (though plans are in the works to develop one). Cybercriminals are swooping in on Android users looking to download Clubhouse by creating their own fake Android version of the app. To add a legitimacy to the scam, the fake app is delivered from a website purporting to b...

Razer has created a concept N95 mask with RGB and voice projection

  Razer claims to have made the world’s smartest mask: its new reusable N95 respirator called Project Hazel. It’s a concept design with a glossy outside shell made of waterproof and scratch-resistant recycled plastic, which is transparent to allow for lip-reading and seeing facial cues when you chat with people. Currently, there isn’t a price or release date attached. Razer refers to Project Hazel as a surgical N95, but it hasn’t yet earned any of the necessary approvals and certifications from the Food and Drug Administration, the Centers for Disease Control and Prevention, or Occupational Safety and Health Administration. In a statement to The Verge , Razer said it is working with a team of medical experts and scientists who are helping to develop the mask. The main features of this mask lie within its two circular zones that flank your mouth. They’re used for ventilation, giving the device an almost futuristic gas mask look. Razer claims Project Hazel will use active disc-type v...

Hackers Compromise Mimecast Certificate For Microsoft Authentication

A sophisticated threat actor compromised a Mimecast certificate used to authenticate several of the company’s products to Microsoft 365 Exchange Web Services, Mimecast disclosed Tuesday. The Lexington, Mass.-based email security vendor said the certificate used to authenticate its Sync and Recover, Continuity Monitor and Internal Email Protect (IEP) products to Microsoft 365 has been compromised. Mimecast said it was recently informed of the compromise by Microsoft. Mimecast’s stock is down $2.40 per share (4.67 percent) to $49 per share in pre-market trading Tuesday, which is the lowest the company’s stock has traded since Dec. 15. Mimecast declined to answer questions about whether the compromise of its certificate was carried out by the same threat actor who for months injected malicious code into the SolarWinds Orion network monitoring tool. Approximately 10 percent of Mimecast’s customers use the compromised connection, according to the company. Of those that do, Mimecast said cu...