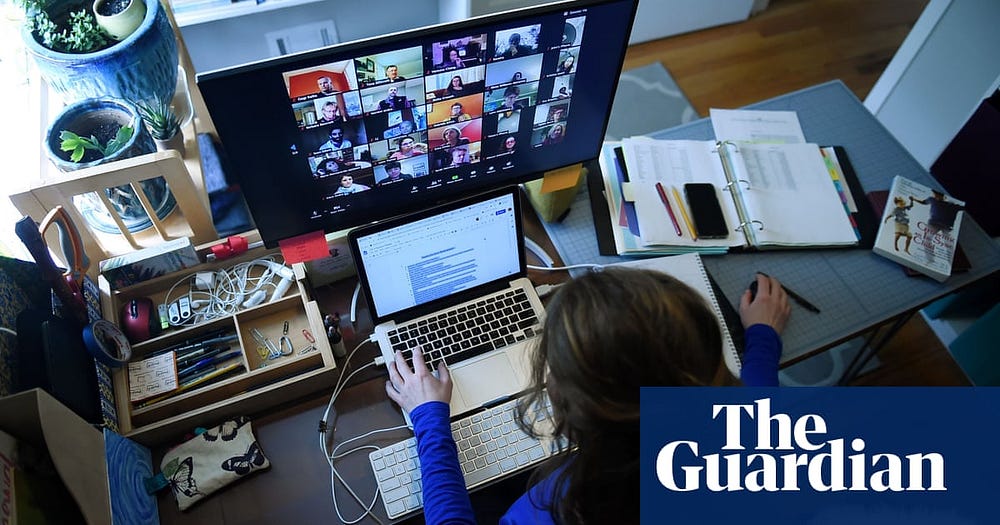
As coronavirus lockdowns have moved many in-person activities online, the use of video conferencing platform Zoom has quickly escalated. So, too, have concerns about its security.
In the last month, there was a 535% rise in daily traffic to the Zoom.us download page, according to an analysis from web analytics firm SimilarWeb. Its app for iPhone has been the most downloaded app in the country for weeks, according to the mobile app market research firm Sensor Tower. Even politicians and other high-profile figures, including the British prime minister, Boris Johnson, and the former US federal reserve chair Alan Greenspan, use it for conferencing as they work from home.
Coronavirus and app downloads: what you need to know about protecting your privacy
But security researchers have called Zoom “ a privacy disaster” and “ fundamentally corrupt “ as allegations of the company mishandling user data snowball.
On Monday, New York’s attorney general, Letitia James, sent a letter to the company asking it to outline the measures it has taken to address security concerns and accommodate the rise in usership.
In the letter, James said Zoom has been slow to address security vulnerabilities “that could enable malicious third parties to, among other things, gain surreptitious access to consumer webcams”. A spokesman from Zoom told the Guardian it is planning to send James the requested information and comply with the request.
“Zoom takes its users’ privacy, security, and trust extremely seriously,” the spokesman said. “During the Covid-19 pandemic, we are working around the clock to ensure that hospitals, universities, schools and other businesses across the world can stay connected and operational.”
Here’s what you need to know about the challenges with Zoom:
‘Zoom bombing’ on the rise
On 30 March, the FBI announced it is investigating increased cases of video hijacking, also known as “Zoom-bombing”, in which hackers infiltrate the video meetings, often shouting racial slurs or threats.
Zoom meetings can be accessed by a short number-based URL, which can easily be generated and guessed by hackers, a January report from the security firm Checkpoint found. Zoom has released guidelines in recent days about how to prevent unwanted guests from crashing video meetings.
No end-to-end encryption
Zoom has falsely advertised itself as using end-to-end encryption, a system that secures communication so that it can only be read by the users involved, a report from the Intercept found. “Currently, it is not possible to enable E2E encryption for Zoom video meetings,” Zoom told the Intercept.
Security flaws
A number of security flaws affecting Zoom have been reported in the past and as recently as this week. In 2009, it was revealed Zoom quietly installed a hidden web server on user devices that could allow the user to be added to a call without their permission.
Another bug discovered this week would enable hackers to take over a Zoom user’s Mac, including tapping into the webcam and hacking the microphone. The number of security issues with Zoom in the past make it as bad as malicious software, said Arvind Narayanan an associate computer science professor at Princeton University.
“Let’s make this simple,” he said. “Zoom is malware.”
In-app surveillance measures
Zoom has been criticized for its “attention tracking” feature, which allows a host to see if a user clicks away from a Zoom window for 30 seconds or more.
This feature would allow employers to check if employees are really tuned into a work meeting or if students are really watching a classroom presentation remotely.
Selling user data
A report from Motherboard found Zoom sends data from users of its iOS app to Facebook for advertising purposes, even if the user does not have a Facebook account.
Zoom changed some of its policies in response. But the story was cited in a lawsuit filed in a federal court in California this week, accusing Zoom of failing to “properly safeguard the personal information of the increasing millions of users” on its platform.
This privacy flaw was also mentioned in the letter from James, which noted such privacy violations could be of particular concern as schools migrate to Zoom for class.
“While Zoom has remediated specific reported security vulnerabilities, we would like to understand whether Zoom has undertaken a broader review of its security practices,” the letter said.
Originally published at https://www.theguardian.com on April 2, 2020.
Comments
Post a Comment