Researcher Demonstrates Several Zoom Vulnerabilities at DEF CON 28


Popular video conferencing app Zoom has addressed several security vulnerabilities, two of which affect its Linux client that could have allowed an attacker with access to a compromised system to read and exfiltrate Zoom user data—and even run stealthy malware as a sub-process of a trusted application.

According to cybersecurity researcher Mazin Ahmed, who presented his findings at DEF CON 2020 yesterday, the company also left a misconfigured development instance exposed that wasn't updated since September 2019, indicating the server could be susceptible to flaws that were left unpatched.

After Ahmed privately reported the issues to Zoom in April and subsequently in July, the company issued a fix on August 3 (version 5.2.4).

It's worth noting that for some of these attacks to happen, an attacker would need to have already compromised the victim's device by other means. But that doesn't take away the significance of the flaws.


In one scenario, Ahmed uncovered an issue with the Zoom Launcher for Linux that could allow an adversary to run unauthorized software owing to the manner it launches the "zoom" executable.

"This breaks all of the protection of application whitelisting, allows malware to run as a subprocess of a trusted vendor (Zoom), and is a bad design/security practice by all means," Ahmed said in an analysis.
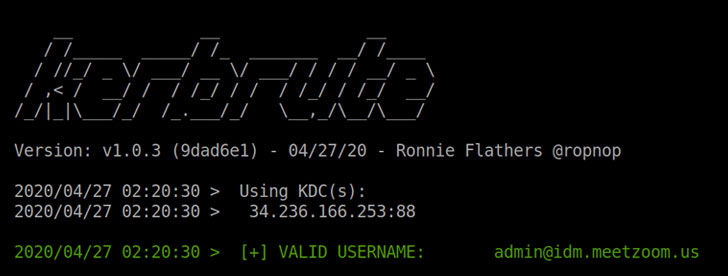
Kerberos authentication

That's not all. In a similar vein, an attacker with access to the victim's machine can read and exfiltrate Zoom user data and configuration by navigating to the local database and even accessing chat messages stored on the system in plaintext format.

Two other flaws involved an externally accessible Kerberos authentication service ("ca01.idm.meetzoom.us") and a TLS/SSL issue that lets malware inject custom certificate fingerprints into the local Zoom database.

"This is per user certificate pinning and intentionally allows for the user to allow custom certificates," Zoom said of the certificate injection flaw. "The user can write to their own database, but no other non-root users can. It's common best practice to have user applications run at their privilege level, as requiring Zoom to run as root would introduce unnecessary security risks to Zoom and our customers."

But it gets more interesting. Ahmed went on to highlight a memory leak vulnerability by exploiting the profile picture feature on Zoom to upload a malicious GIF image, download the rendered file, and extract data from it to leak portions of system memory.
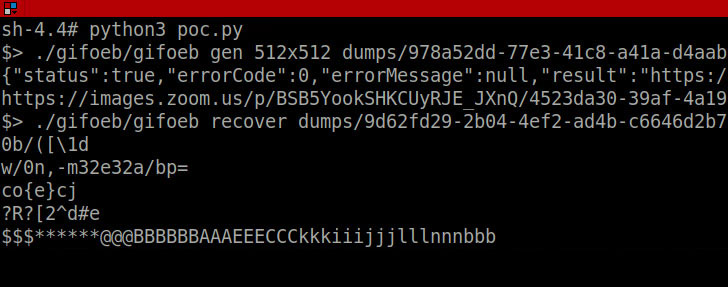
image memory vulnerability

"After an internal investigation, we've concluded that the behavior was not a memory leak but just our image utility's best effort at converting a malformed gif into a jpeg," the company said.

Although Ahmed believes this to be a consequence of a known flaw in ImageMagick image conversion software (CVE-2017-15277), Zoom has said it doesn't use the utility to convert GIFs uploaded as profile pictures into JPEG format.
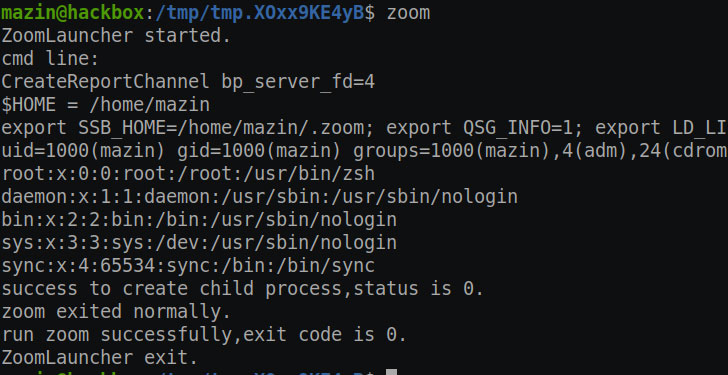
Zoom Vulnerabilities

In response to the disclosures, Zoom has taken down the exposed Kerberos authentication server to prevent brute-force attacks, while also acknowledging that it's working on addressing the lack of encryption while storing the chat logs.

It's recommended that users update Zoom to the latest version to mitigate any risk arising out of these issues.

"We thank Mazin for reporting his findings. We have fixed all relevant issues and recommend that users keep their Zoom clients up to date to ensure they receive ongoing security and product updates. Zoom appreciates vulnerability reports from researchers. If you think you've found a security issue with Zoom products, please send a detailed report to security@zoom.us," a spokesperson for the company told The Hacker News.

The development came as the company resolved a security flaw last month. It allowed attackers to crack the numeric passcode used to secure private meetings on the platform and eavesdrop on participants.

The article is taken from: https://thehackernews.com/

Comments

Popular posts from this blog

Bogus Android Clubhouse App Drops Credential-Swiping Malware

The malicious app spreads the BlackRock malware, which steals credentials from 458 services — including Twitter, WhatsApp, Facebook and Amazon. Researchers are warning of a fake version of the popular audio chat app Clubhouse, which delivers malware that steals login credentials for more than 450 apps. Clubhouse has burst on the social media scene over the past few months, gaining hype through its audio-chat rooms where participants can discuss anything from politics to relationships. Despite being invite-only, and only being around for a year, the app is closing in on 13 million downloads . However, as of now the app is only available on Apple’s App Store mobile application marketplace — there’s no Android version yet (though plans are in the works to develop one). Cybercriminals are swooping in on Android users looking to download Clubhouse by creating their own fake Android version of the app. To add a legitimacy to the scam, the fake app is delivered from a website purporting to b...

Razer has created a concept N95 mask with RGB and voice projection

  Razer claims to have made the world’s smartest mask: its new reusable N95 respirator called Project Hazel. It’s a concept design with a glossy outside shell made of waterproof and scratch-resistant recycled plastic, which is transparent to allow for lip-reading and seeing facial cues when you chat with people. Currently, there isn’t a price or release date attached. Razer refers to Project Hazel as a surgical N95, but it hasn’t yet earned any of the necessary approvals and certifications from the Food and Drug Administration, the Centers for Disease Control and Prevention, or Occupational Safety and Health Administration. In a statement to The Verge , Razer said it is working with a team of medical experts and scientists who are helping to develop the mask. The main features of this mask lie within its two circular zones that flank your mouth. They’re used for ventilation, giving the device an almost futuristic gas mask look. Razer claims Project Hazel will use active disc-type v...

Hackers Compromise Mimecast Certificate For Microsoft Authentication

A sophisticated threat actor compromised a Mimecast certificate used to authenticate several of the company’s products to Microsoft 365 Exchange Web Services, Mimecast disclosed Tuesday. The Lexington, Mass.-based email security vendor said the certificate used to authenticate its Sync and Recover, Continuity Monitor and Internal Email Protect (IEP) products to Microsoft 365 has been compromised. Mimecast said it was recently informed of the compromise by Microsoft. Mimecast’s stock is down $2.40 per share (4.67 percent) to $49 per share in pre-market trading Tuesday, which is the lowest the company’s stock has traded since Dec. 15. Mimecast declined to answer questions about whether the compromise of its certificate was carried out by the same threat actor who for months injected malicious code into the SolarWinds Orion network monitoring tool. Approximately 10 percent of Mimecast’s customers use the compromised connection, according to the company. Of those that do, Mimecast said cu...